From hundreds of findings to the few that matter.
Ranked by real-world exploitation, not severity alone.
308 findings, sorted by severity. Nine of the 308 findings shown. 3 packages need fixing first, starting with vm2.
vm2 3.9.11 → 3.9.17Likely to be exploited · CriticalFix first
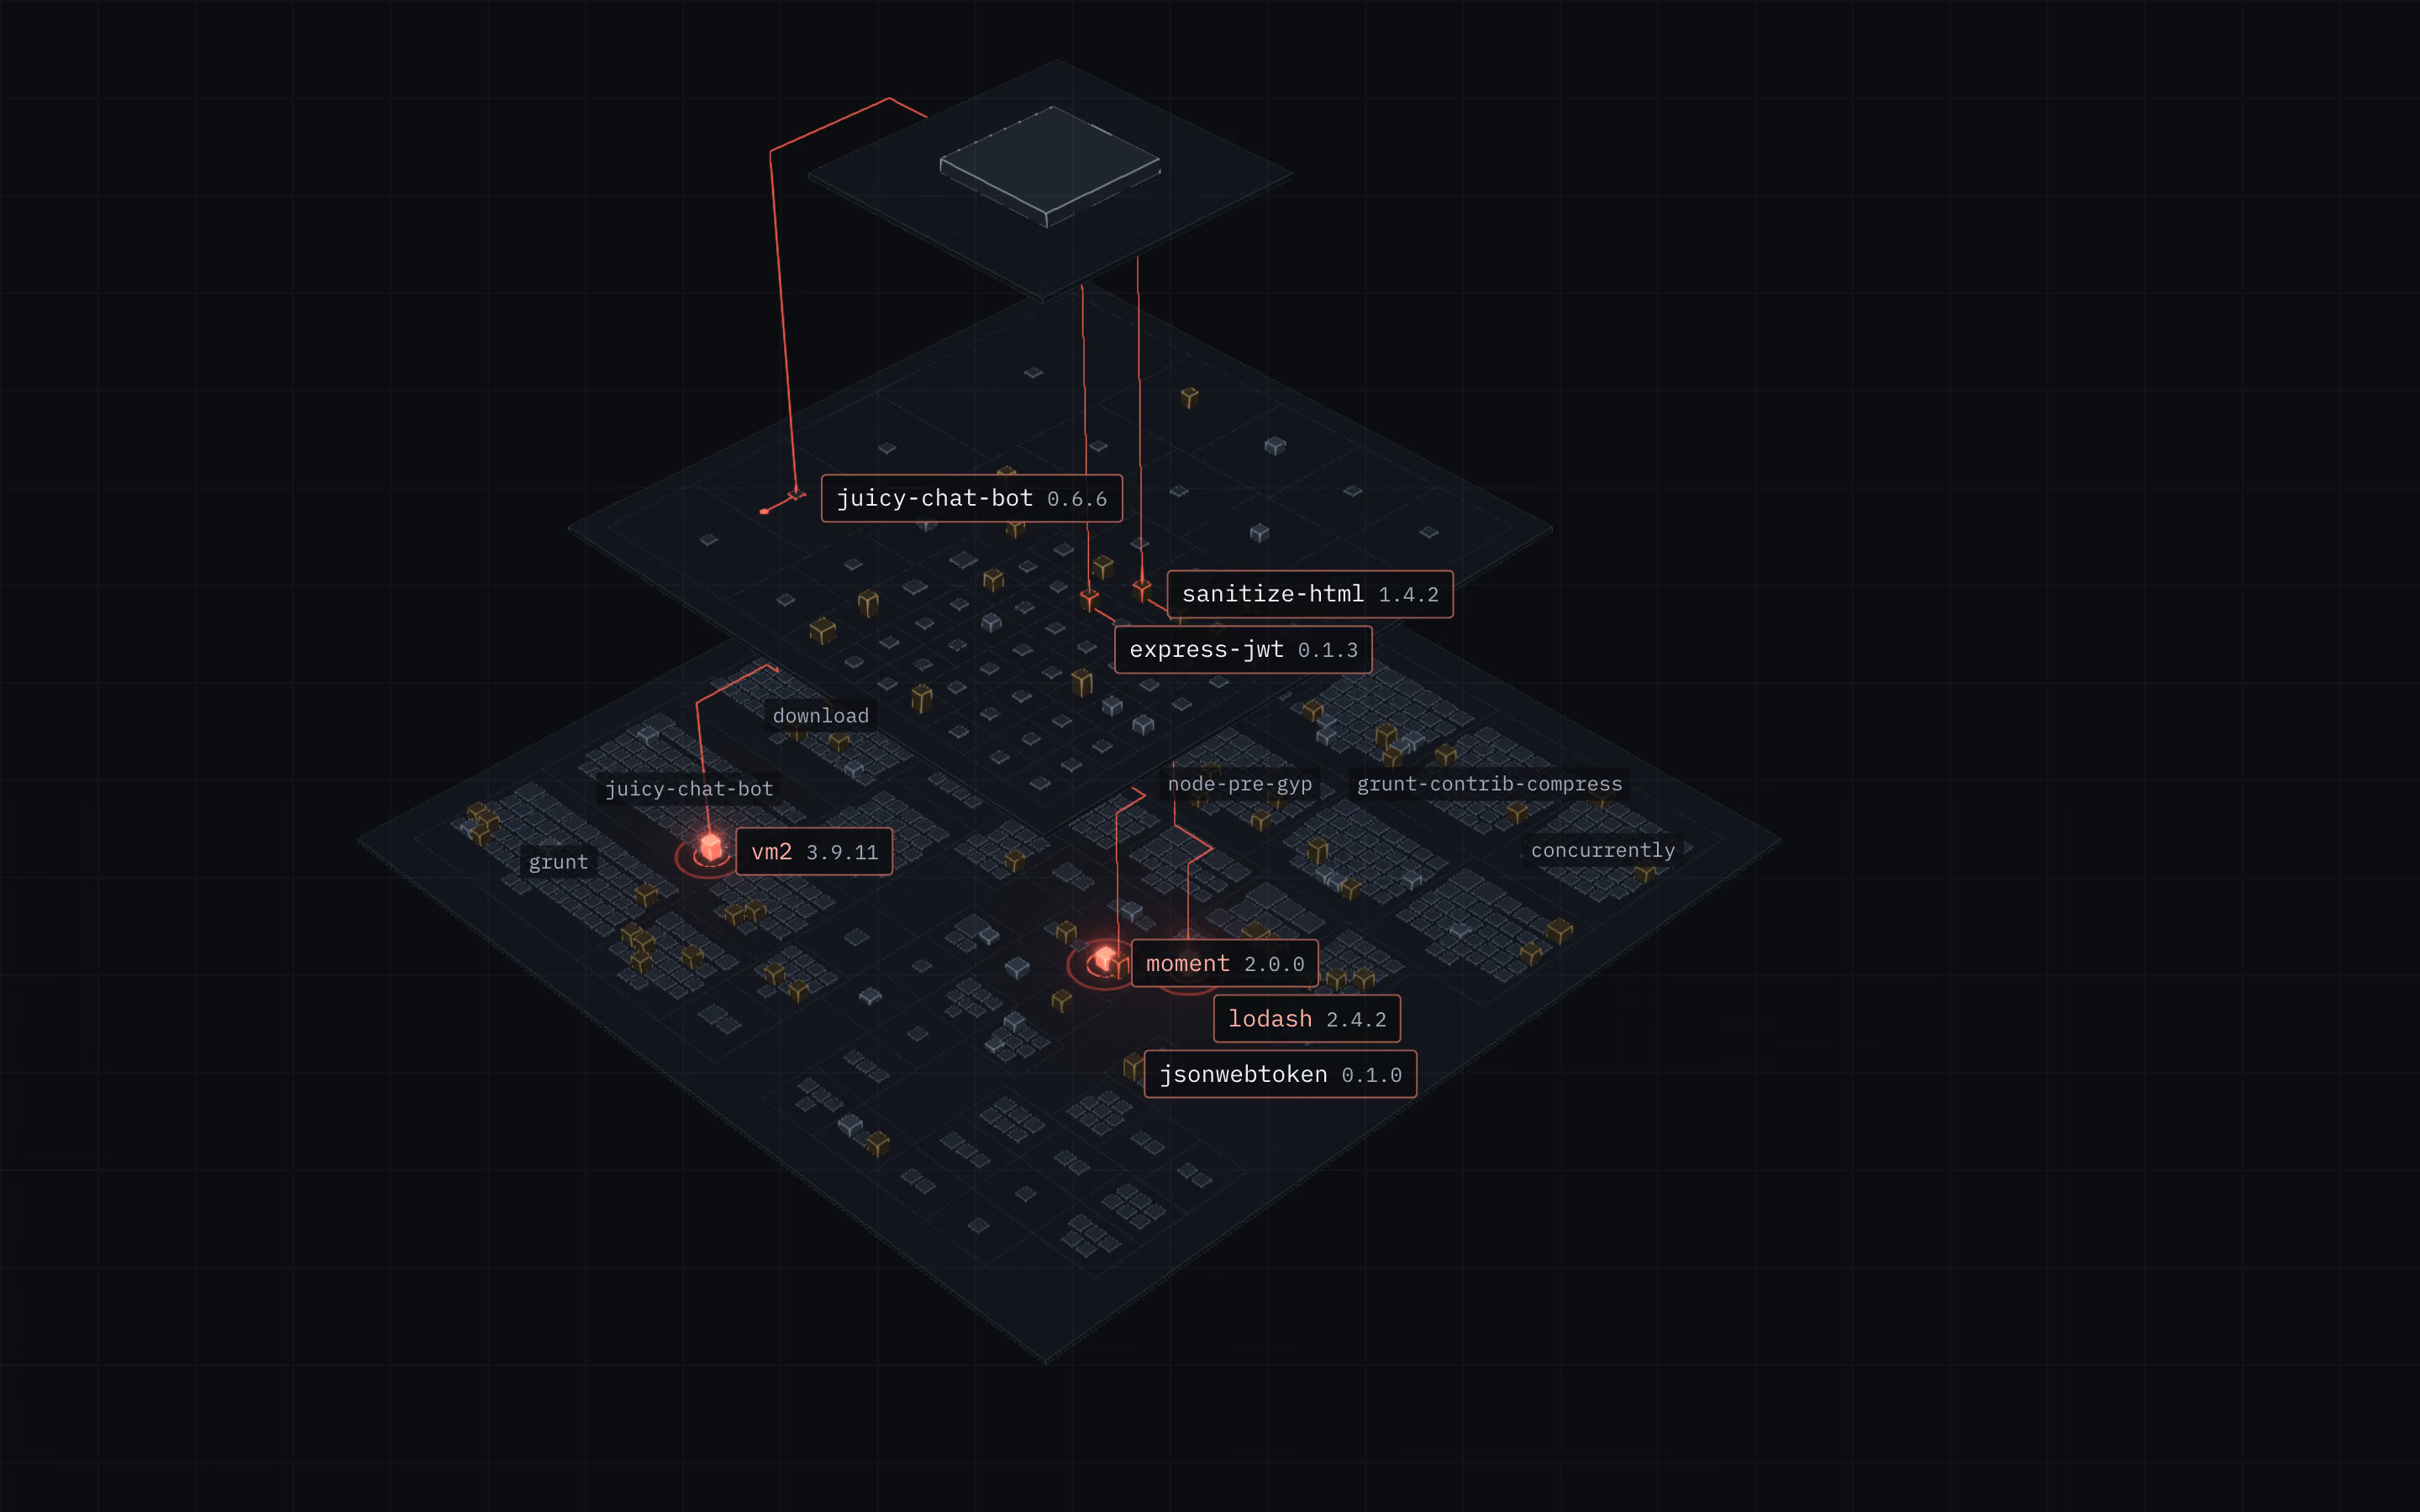
Trace any package to its source.
Every dependency, layer by layer, with the path that brought it in.

Path to the app
- juice-shopYour code
- juicy-chat-bot 0.6.6Direct
- vm2 3.9.11Transitive
Pulled in by juicy-chat-botPulls in 2 packages
The exact upgrade, before you make it.
The version to upgrade to and every package that changes with it.
npm · Composer
laravel/frameworkLarge
5.8.31 → 6.20.45 · PHP 7.2.5 or later18 packages change16 existing, 2 new
nesbot/carbon2.22.3 → 2.31.0
beyondcode/laravel-dump-server1.2.2 → 1.3.0
symfony/* (8)4.3.3 → 4.3.4
league/commonmarknew · 1.3.0
Ready for your coding agent.
Every fix comes with a prompt your agent can run and verify.
› Upgrade laravel/framework from 5.8.31 to 6.20.45 …
- Edited composer.json, 2 lines
- composer update: 16 updated, 2 installed
- vendor/bin/phpunit: OK
- composer audit: CVE-2024-52301 no longer listed
laravel/framework is 6.20.45. Nothing committed.
Exploitation data, not guesswork.
Known malware, CISA KEV, public exploits and EPSS for every public package.
How ranking works- Known malware
- Known malicious versions
- CISA KEV
- Exploited in the wild
- Public exploits
- Metasploit and nuclei
- EPSS
- Likelihood in 30 days
- vm2 3.9.11EPSS 73.0%
- lodash 2.4.2Public exploit · nuclei
- moment 2.0.0EPSS 13.9%
- minimist 0.2.3No known exploit
Works with your stack.
- npm
- pnpm
- Yarn
- Bun
- Composer
- Poetry
- uv
- Pipenv
- pip
- Bundler
- Go
- Cargo
- Gradle
- CycloneDX
- SPDX
Your lockfile. Never your code.
Only lockfiles, manifests, SBOMs and version files are read. Uploads aren’t stored.
Privacy- package-lock.jsonRead
- src/Never read